Platform module
Approvals & Workflow
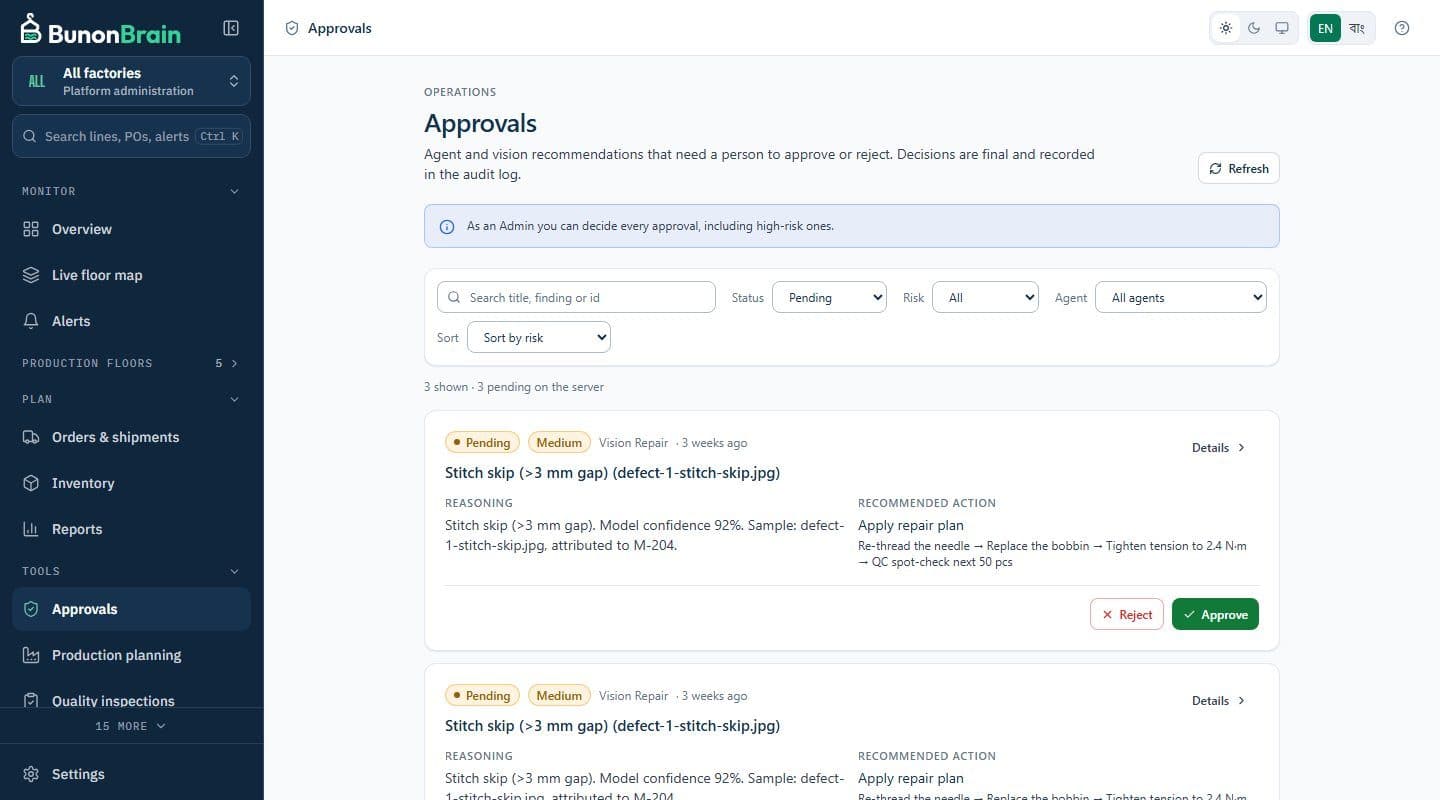
Risky actions wait in an approval queue instead of happening automatically. The server checks the approver's role and the risk tier, requires a reason to reject, and writes every decision to an append-only audit log.
The problem it solves
Why this module exists
When software can change a plan or move people between lines, someone accountable has to agree first, and there must be a record of who decided what and why.
How it works
Approvals & Workflow, step by step
- 01
Propose
Agents, production plans and line-balancing proposals create approval requests with a risk tier.
- 02
Decide
An authorised person approves or rejects. High-risk items need a higher permission, and rejection needs a reason.
- 03
Record
Each decision is written to the audit log in the same transaction. The audit table rejects edits and deletes at the database level.
Key capabilities
What it does
Risk tiers
Low, medium and high risk, with separate permissions for high-risk decisions.
Server-side enforcement
Permissions are checked by the API on every request, not just hidden in the interface.
Append-only audit log
Decisions, role changes and settings changes are recorded and cannot be edited through the application.
Who benefits
Factory Manager
One queue of decisions, ordered by risk.
Administrators
A tamper-resistant record for internal review.
Next step
See BunonBrain on a running garment plant
We walk you through the product on a simulated factory and answer questions about your own lines.